

The short answer
An ISO 27001 checklist is a working list for checking readiness against ISO/IEC 27001:2022: every management system clause from 4 to 10, the Annex A controls your Statement of Applicability selects, and the evidence an auditor will sample. Rate each line met, partly met or not met, then use the audit checklist before booking Stage 1.
On this page
- How do you use this ISO 27001 checklist?
- ISO 27001 self-assessment: score your readiness
- ISO 27001 requirements checklist: are clauses 4 to 10 ready?
- Documents and records to have ready
- Annex A checklist: the four themes
- ISO 27001 audit checklist: what will the auditor check?
- Why Sovereign Secure
- Download the ISO 27001 checklist (.xlsx)
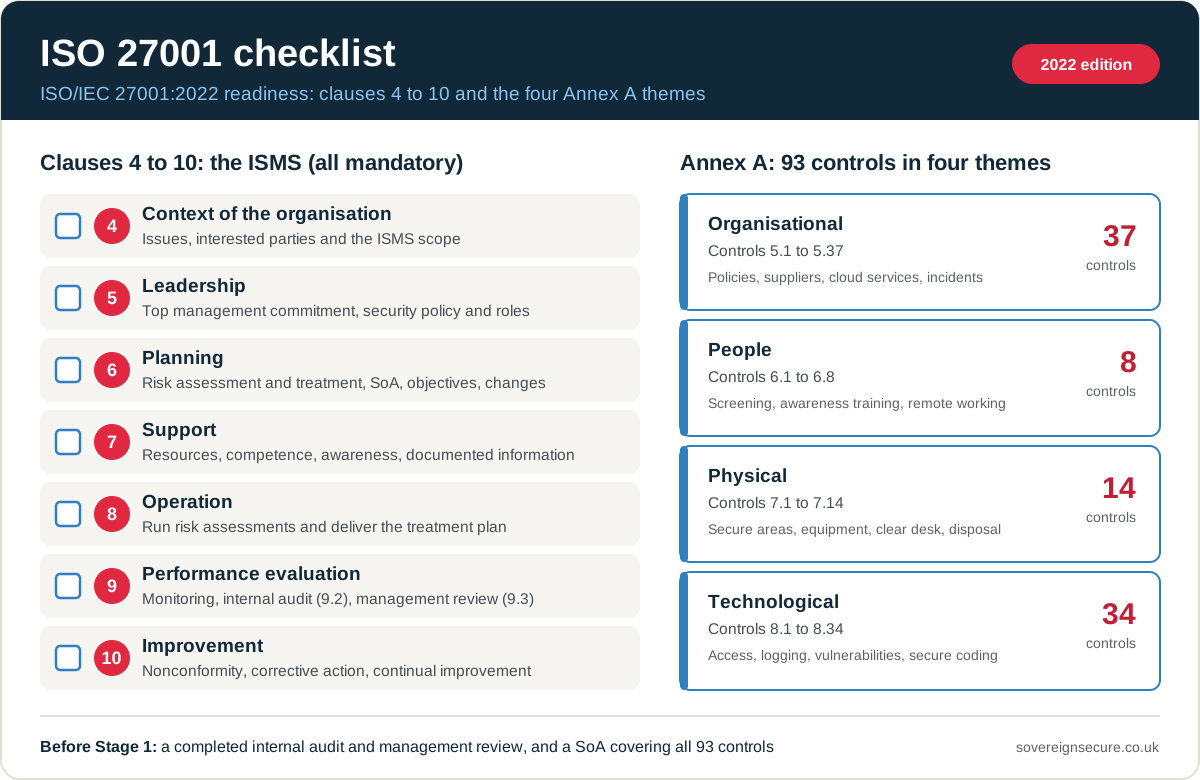
This ISO 27001 checklist turns ISO/IEC 27001:2022 into two working lists: a readiness checklist for the seven management system clauses (4 to 10) and the four Annex A themes, and an audit checklist for the certification audit. Use the first as your ISO 27001 compliance checklist while you build the ISMS, and the second before you book Stage 1. Every clause is mandatory. Annex A controls are included or excluded, with a reason, in your Statement of Applicability (SoA).
Sovereign Secure Ltd is an ISO 27001-certified UK consultancy, a PCI SSC-approved QSA company and an IASME-licensed Cyber Essentials certification body. We built this checklist from the 2022 standard, including Amendment 1 (2024). Certification audits for our clients are carried out by an independent certification body, our partner MQA International.
How do you use this ISO 27001 checklist?
Use it as a self-assessment first, then as your evidence tracker up to the certification audit. For each line:
- Rate it: met, partly met, not met or not applicable. Only Annex A controls can be not applicable; clauses 4 to 10 cannot be excluded.
- Name the evidence. A policy on its own rarely satisfies an auditor. They ask for records that show the control operates: dated reviews, tickets, logs and sign-offs.
- Give each gap an owner and a date. Anything not met becomes an action on your risk treatment plan.
A checklist shows where you stand; it does not replace a risk assessment. Your controls should follow from the risks you identify under clause 6.1.2, not the other way round. Once you know the gaps, our ISO 27001 implementation guide sets out the steps to close them in order.
ISO 27001 self-assessment: score your readiness
An ISO 27001 self-assessment, often called an ISO 27001 readiness assessment, is the quickest way to see how far you are from certification. Work through the clause 4 to 10 checklist below, or the “Clauses 4 to 10” sheet of the spreadsheet, and score every line honestly, based on the evidence you could show an auditor today rather than what you intend to do.
The spreadsheet rates each line Met, Partly met or Not met. If you prefer a number for a board report or a readiness assessment, use this 0 to 3 scale, where scores 1 and 2 both count as Partly met in the spreadsheet:
| Score | Meaning | Spreadsheet rating |
|---|---|---|
| 0 | Nothing in place yet | Not met |
| 1 | Documented or planned, but not yet operating | Partly met |
| 2 | Operating, but records are incomplete or not yet reviewed | Partly met |
| 3 | Operating, with dated records an auditor could sample | Met |
As a rough guide to what your scores mean:
| What you see | What it usually means | Next step |
|---|---|---|
| Mostly 0s and 1s | The ISMS is at an early stage | Agree the scope, then run the risk assessment before writing more policies |
| Mostly 2s, some 1s | The design is there; the evidence is not yet | Run the controls long enough to build records, then hold the internal audit and management review |
| 3s across clauses 4 to 10, including 9.2 and 9.3 | Close to ready | Work through the audit checklist below, then book Stage 1 |
A self-assessment has one weakness: teams tend to score a control as met when a policy exists, while an auditor asks for proof that it operates. Book an ISO 27001 gap analysis when you cannot judge your own scores, when a customer deadline is fixed, or before you commit budget, so an outside assessor samples the evidence and ranks each gap by risk.
ISO 27001 requirements checklist: are clauses 4 to 10 ready?
Clauses 4 to 10 define the information security management system (ISMS) itself, and none can be excluded. Tick each row once the evidence exists. For what each clause means and why it is there, see our guide to ISO 27001 requirements.
| Clause | Check | Evidence to have ready |
|---|---|---|
| ☐ 4.1 | Internal and external issues affecting the ISMS identified, including whether climate change is relevant | Context or issues register |
| ☐ 4.2 | Interested parties and their requirements listed, and which ones the ISMS will address | Interested parties register |
| ☐ 4.3 | Scope set, with boundaries, interfaces and dependencies | ISMS scope statement |
| ☐ 4.4 | ISMS processes and how they interact defined | Process map or ISMS manual |
| ☐ 5.1 | Top management sets direction, provides resources and builds the ISMS into business processes | Board minutes, approved budget, named sponsor |
| ☐ 5.2 | Information security policy approved, communicated and available | Signed policy, communication record |
| ☐ 5.3 | Roles, responsibilities and authorities assigned, including who reports on ISMS performance | Role descriptions or RACI |
| ☐ 6.1.1 | Risks and opportunities affecting the ISMS itself planned for | Actions in the ISMS plan |
| ☐ 6.1.2 | Risk assessment method set, with acceptance criteria and named risk owners, giving consistent results | Risk methodology, risk register |
| ☐ 6.1.3 | Treatment chosen, controls compared with Annex A, plan approved by risk owners | SoA, risk treatment plan |
| ☐ 6.2 | Measurable objectives set, with owners, resources and deadlines | Objectives register |
| ☐ 6.3 | Changes to the ISMS carried out in a planned way (new in 2022) | Change records |
| ☐ 7.1 | Resources for the ISMS provided | Budget, role allocation |
| ☐ 7.2 | Competence defined and evidenced for people who affect security | Training records, qualifications |
| ☐ 7.3 | Staff know the policy, their part in it and the consequences of not following it | Awareness training completion |
| ☐ 7.4 | What, when, with whom and how to communicate decided | Communication plan |
| ☐ 7.5 | Documents approved, version-controlled, protected and available | Document register, version history |
| ☐ 8.1 | Processes run to defined criteria; outsourced processes and changes controlled | Procedures, supplier controls, change records |
| ☐ 8.2 | Risk assessments repeated at planned intervals and after significant change | Dated assessment results |
| ☐ 8.3 | Risk treatment plan implemented | Closed actions, updated register |
| ☐ 9.1 | What to monitor and measure decided, and results analysed | Metrics and analysis records |
| ☐ 9.2 | Internal audit programme covers the whole ISMS, run by objective auditors | Audit programme and reports |
| ☐ 9.3 | Management review held with every required input, decisions recorded | Review minutes |
| ☐ 10.1 | ISMS continually improved | Improvement log |
| ☐ 10.2 | Nonconformities corrected, root causes found, corrective action checked for effectiveness | Corrective action log |
Certification bodies expect at least one completed internal audit (9.2) and management review (9.3) before they certify you, so schedule both early.
Documents and records to have ready
ISO 27001:2022 makes a defined set of documents and records mandatory, from the ISMS scope (4.3) and information security policy (5.2) to internal audit and management review results (9.2 and 9.3), and applicable Annex A controls add more, such as an asset inventory. The full list, with the clause behind each item, is on our ISO 27001 requirements page, and our free ISO 27001 toolkit gives you templates for the information security policy, the Statement of Applicability and the risk register. Use the evidence column in the table above, or the Documents sheet in the spreadsheet version of this checklist, to tick each one off.
Annex A checklist: the four themes
Check each Annex A control against your risk assessment and record the decision in your SoA: if it treats an identified risk, or a law or contract demands it, mark it applicable. Our free Statement of Applicability template lists all 93 controls with a column for each decision. The 93 controls fall into four themes: organisational (5.1 to 5.37), people (6.1 to 6.8), physical (7.1 to 7.14) and technological (8.1 to 8.34). Our guide to ISO 27001 controls explains every control in plain English and what changed from the 2013 edition, whose transition period ended on 31 October 2025.
Two checks catch out smaller organisations:
- Remote-first teams. A company without its own office may exclude several physical controls, but 7.7, 7.9, 7.10 and 7.14 usually still apply because staff work on laptops at home. Where systems run in a public cloud, evidence the provider’s physical security through supplier controls 5.19 to 5.23, for example with its own ISO 27001 certificate.
- Cyber Essentials holders. If you hold Cyber Essentials, you already have evidence for firewalls (8.20), secure configuration (8.9), security update management (8.8), user access control (5.15 to 5.18, 8.2, 8.5) and malware protection (8.7). See how the two schemes fit together in Cyber Essentials vs ISO 27001.
For 8.8 and 8.29, auditors ask how you find weaknesses; our guide to ISO 27001 penetration testing explains what counts as evidence.
ISO 27001 audit checklist: what will the auditor check?
Certification runs in two stages, both carried out by an independent certification body. Stage 1 checks that your ISMS is designed and documented; Stage 2 checks that it works in practice. This audit checklist covers what to have ready for each stage; our guide to the ISO 27001 audit explains how Stage 1, Stage 2 and the surveillance audits run.
| Aspect | Stage 1 audit | Stage 2 audit |
|---|---|---|
| Focus | ISMS design and readiness | Controls operating as described |
| What the auditor reviews | Scope, policy, risk method, SoA, risk treatment plan, internal audit and management review | Interviews, walkthroughs and samples of records across the clauses and applicable controls |
| Common problems | SoA does not match the risk treatment plan; unclear scope; no internal audit yet | Controls documented but no records; corrective actions left open; staff unaware of policy |
| Outcome | Go-ahead for Stage 2, or issues to fix first | Certification recommendation once major nonconformities are closed and corrective action plans for minor ones are accepted |
Before booking Stage 1, tick these off:
- Scope statement agreed, covering the services your customers ask about
- Risk register complete, with owners and acceptance decisions
- SoA covers all 93 controls, with a justification for each inclusion and exclusion
- Policies approved and communicated, with records to prove it
- At least one internal audit completed across the whole ISMS (9.2)
- Management review held and minuted (9.3)
- Internal audit findings logged with corrective actions
- Evidence filed by clause and control, so any record can be found quickly
Clause 9.2 needs an auditor who is objective and impartial. If nobody in-house is trained and independent of the work, an outsourced ISO 27001 internal audit covers it.
Why Sovereign Secure
- ISO 27001 certified ourselves, so we know what certification auditors ask for.
- Preparation and certification kept separate. We get you ready through our ISO 27001 consultancy; certification audits are carried out by an independent certification body, our partner MQA International.
- One evidence set for several schemes. As a PCI QSA company and IASME Cyber Essentials certification body, we map Annex A to PCI DSS and Cyber Essentials.
- Testing from the same provider for Annex A 8.8 and 8.29, from penetration testing to vulnerability scanning.
- UK company since 2012, headquartered in Accrington, Lancashire (Companies House 08334453).
Download the ISO 27001 checklist (.xlsx)
Download the ISO 27001 checklist (.xlsx), free to use and adapt within your organisation. It turns this page into a working spreadsheet, with dropdowns for rating and status, and columns for owners, dates and notes:
- Clauses 4 to 10: all 25 lines from the table above, with a plain-English summary of each requirement, the evidence to have ready and whether the clause requires documented information.
- Annex A themes: the four themes, how many controls your SoA marks applicable or excluded, and the checks for remote-first teams, cloud hosting, Cyber Essentials holders and testing.
- Audit checklist: the Stage 1 items above, plus the Stage 2 checks.
- Documents: the mandatory documents and records, and those that common Annex A controls add.
- Summary: live counts by status and rating, progress clause by clause and whether every Stage 1 item is done.
Need help completing it? Use the form below, which is already set to ISO 27001.
Prefer an expert to score it? Book an ISO 27001 gap analysis for a risk-ranked roadmap. If you want help with the whole project, our guide to choosing an ISO 27001 consultant covers what to look for and the questions to ask. To budget for the whole project, see ISO 27001 certification cost, or call +44 161 523 5276.
Your next step
Last reviewed October 2026 by the Sovereign Secure assessment team.














